Hello! In our last lesson, we focused on verifying and troubleshooting Access Control Lists (ACLs) to ensure your network security policies are working exactly as intended. We saw how ACLs act as filters, deciding what traffic is allowed or denied. Now, we'll shift our focus to another critical networking technology that your project will rely on: Network Address Translation (NAT).
While ACLs control what traffic can pass through your router, NAT controls how that traffic appears to the outside world. It's the technology that allows the many devices on your private network, each with a private IP address, to communicate with the internet using a limited number of public IP addresses. This lesson introduces the fundamental purpose of NAT and the specific terminology Cisco uses to describe the addresses involved in the translation process.
The Problem: IPv4 Address Exhaustion
The internet was built on IPv4, which provides approximately 4.3 billion unique addresses. While that sounds like a lot, the explosion of internet-connected devices has nearly exhausted this address space. Network Address Translation, in conjunction with private addressing, was developed as a powerful solution to this problem, dramatically extending the life of IPv4.
To start, let's explore why NAT is necessary and the concept of private IP addresses.
Free CCNA | NAT (Part 1) | Day 44 | CCNA 200-301 Complete Course
The video "Free CCNA | NAT (Part 1)" from Jeremy's IT Lab provides an excellent introduction to the problem NAT solves.
Watch the first two segments of the video: Begin with the introduction to private IPv4 addresses. Pay close attention to the RFC 1918 address ranges. You're likely familiar with these, but this is a good, quick review. The key point is that these addresses cannot be routed over the public internet. Continue with the introduction to NAT's purpose. The video explains how NAT allows devices with these private addresses to "borrow" a public address to communicate with the internet.
As the video explains, organizations are free to use private IP addresses (like 10.x.x.x, 172.16.x.x - 172.31.x.x, and 192.168.x.x) for their internal networks. This allows for millions of devices in private networks around the world to use the same IP addresses without conflict. However, when a device on your private network needs to access a server on the public internet, its private source IP address must be translated into a unique, public IP address. This translation process is the core function of NAT.
The Language of NAT: Four Key Terms
When a router performs NAT, it needs a precise way to refer to the addresses involved, especially since the "source" and "destination" addresses change depending on the direction of the traffic (request vs. reply). To eliminate this ambiguity, Cisco developed a specific set of four terms. Understanding these is crucial for configuring and troubleshooting NAT.
The terms are built from two pairs of words:
- Inside / Outside: This pair describes the location of the host. Is it on your internal, private network (inside) or on the external, public network (outside)?
- Local / Global: This pair describes the perspective. Is it the address as seen from the private network (local) or the address as seen from the public internet (global)?
Combining these gives us the four essential NAT terms.
Cisco NAT Terminology – Practical Networking .net
This article from PracticalNetworking.net does a superb job of breaking down these potentially confusing terms with a clear diagram and explanation.
Start by reading the section "Cisco Terminology" to understand the definitions of Inside vs. Outside and Local vs. Global. Next, carefully study the diagram and the breakdown of each of the four terms that follows it. This will walk you through a static NAT example, labeling each address involved.
To solidify this, let's look at the animated diagram from the article you just read. It illustrates a typical communication flow where an internal PC (10.1.1.11) communicates with an external web server (82.6.4.2).
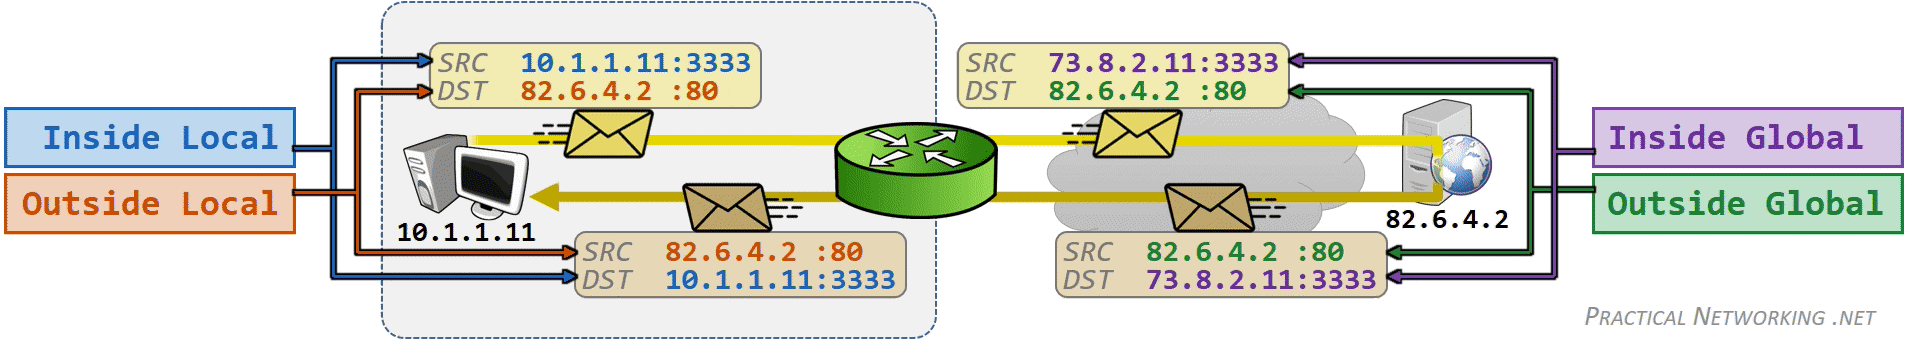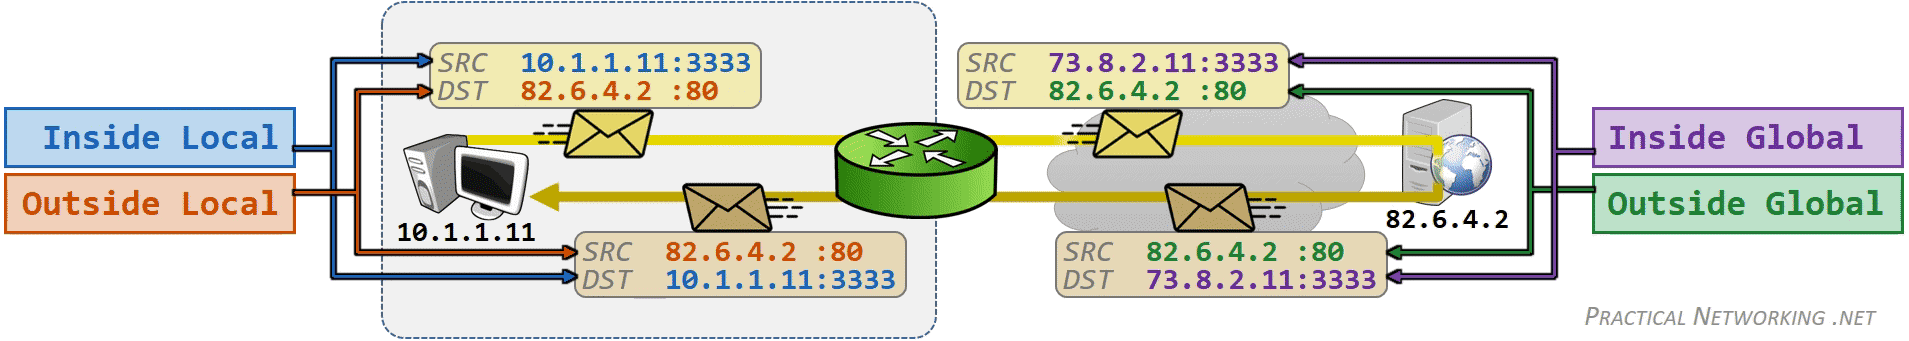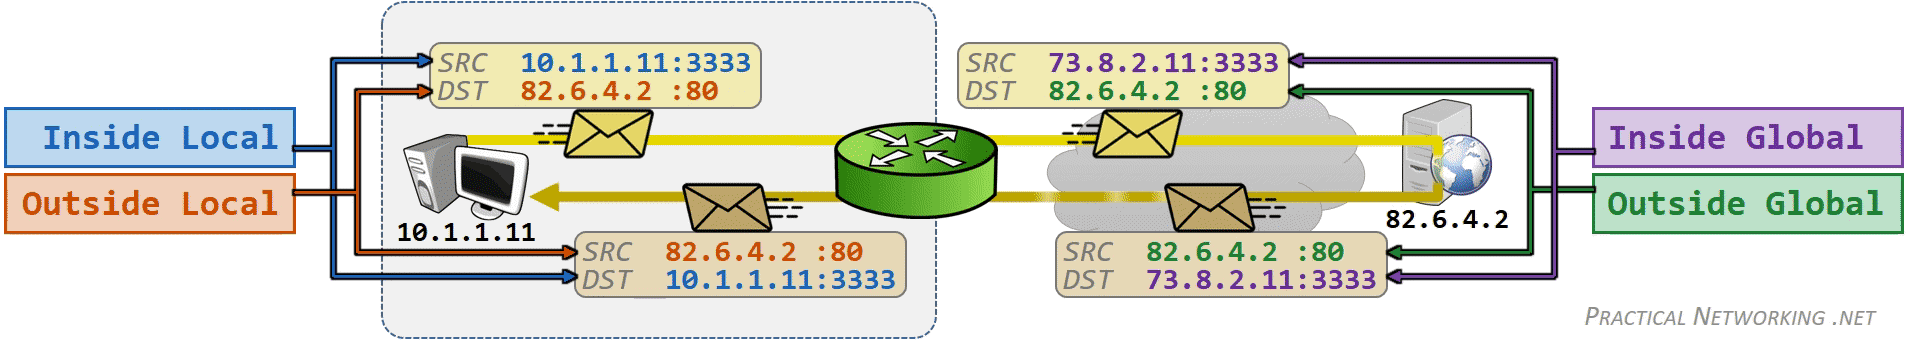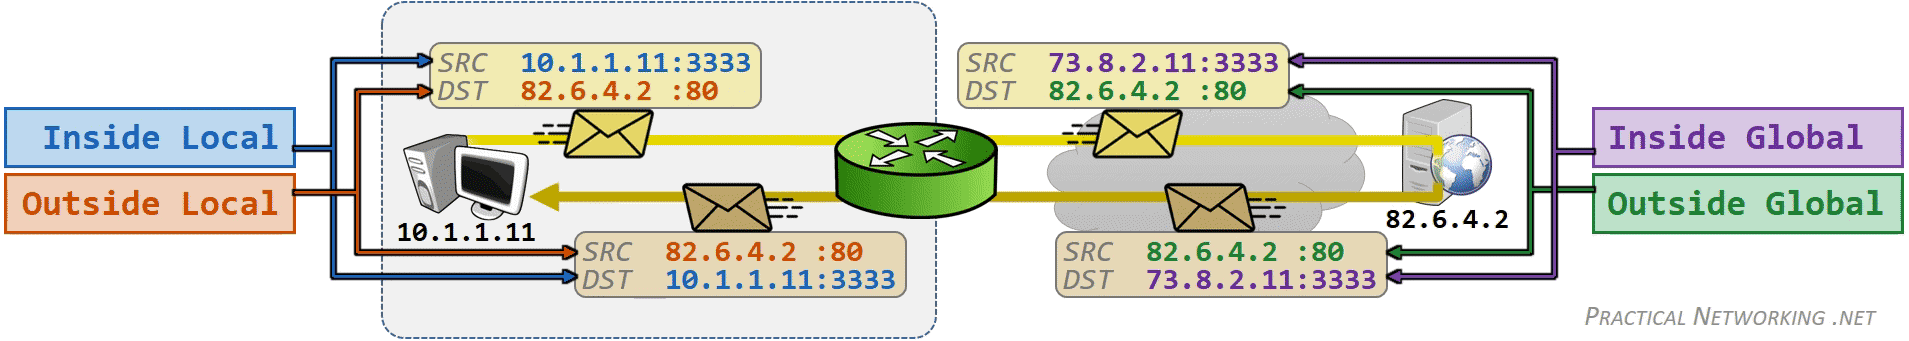
Let's break down the addresses in this diagram:
- Inside Local Address (10.1.1.11): The private IP address actually configured on the host inside your network. It's the address from the local perspective.
- Inside Global Address (73.8.2.11): The public IP address that represents the inside host to the rest of the world. It's the address of the inside host from a global perspective.
- Outside Global Address (82.6.4.2): The public IP address of the host on the outside network (the web server). This is its true, globally reachable address.
- Outside Local Address (82.6.4.2): The IP address of the outside host as it appears to the inside network. In most cases, including this one, this is the same as the Outside Global address. It would only be different if you were also translating the destination address, a less common scenario not covered in the CCNA exam.
Seeing the Terms in Practice
Now that you have a grasp of the terminology, let's see how it applies in a router's NAT translation table. The following video segment defines these terms again and shows you exactly where they appear in the output of the show ip nat translations command.
Free CCNA | NAT (Part 1) | Day 44 | CCNA 200-301 Complete Course
Return to Jeremy's IT Lab video to see these concepts applied.
Watch the segment from Static NAT and NAT Terms. Focus on the clear definitions provided for each of the four address types and how they correspond to the columns in the show ip nat translations output table. This connects the theory directly to the command-line interface you'll use in your project.
Check Your Understanding
Let's test your understanding of these new terms. The video you've been watching includes a quiz. Try to answer the final question, which directly addresses this lesson's learning outcome.
Free CCNA | NAT (Part 1) | Day 44 | CCNA 200-301 Complete Course
This section of the video contains several quiz questions.
Fast forward to quiz question 5. Pause the video and, based on the network diagram shown, identify the Inside Local, Inside Global, Outside Local, and Outside Global addresses before the answer is revealed.
Conclusion
In this lesson, we established the fundamental purpose of NAT as a solution to IPv4 address exhaustion and as a mechanism to connect private networks to the public internet. We then dissected the four key terms—Inside Local, Inside Global, Outside Local, and Outside Global—that are essential for understanding, configuring, and troubleshooting NAT on Cisco devices.
Key Takeaways:
- NAT's Purpose: To translate private, non-routable IP addresses into public, globally unique IP addresses, allowing internal hosts to access the internet.
- Inside vs. Outside: Describes the physical location of a host relative to your network.
- Local vs. Global: Describes the address from the perspective of either the inside (local) or outside (global) network.
- Inside Local: The private IP of an internal host.
- Inside Global: The public IP that represents an internal host to the internet.
- Outside Global: The public IP of an external host.
- Outside Local: The IP of an external host as seen from the inside (usually the same as Outside Global).
With this foundational terminology in place, you are now ready to learn how to configure NAT. In our next lesson, we will cover the configuration and verification of Static NAT, which creates a one-to-one mapping between an inside local and an inside global address.