Recommended resources
The freely available resources this lesson will direct you to.
- Deep Dive on Microsoft Entra Private Accesswww.youtube.com
- Secure Cloudflare Tunnels with vLANs and an Internal Firewall Before It's Too Late!www.youtube.com
- [PDF] Enabling Zero Trust Architecture (ZTA) with - OWASP Foundationowasp.org
- Microsoft Entra Private Network Connectors - Global Secure Accesslearn.microsoft.com
Hello! Welcome to the next lesson in our series on architecting security products.
In our last session, we designed the "brain" of our ZTNA service: the policy engine. We saw how it acts as a real-time data processing system, ingesting identity, device, and contextual signals to compute a dynamic trust score and make access decisions. This all happens within the ZTNA provider's cloud, which we call the control plane.
This raises a critical question: how does a policy decision made in the cloud grant a user access to a private application running deep inside an enterprise network, without exposing that network to the internet? The answer lies in the component we will design today.
This lesson directly addresses the learning outcome: Design the architecture of ZTNA connectors, focusing on outbound-only connectivity and secure registration with the control plane. We will architect the secure, lightweight agent that acts as a bridge between the cloud-based control plane and the on-premises data center or private cloud.
1. The Role of the Connector in ZTNA
The ZTNA connector is a piece of software installed within the private network where the applications reside. Its job is to provide a secure path for authorized user traffic to reach a specific application, but only after the ZTNA control plane has brokered the connection.
This "service-initiated" model is a cornerstone of ZTNA. The diagram below illustrates the connector's place in the architecture.

The connector is fundamentally a stateless proxy that is deployed "close" to the application it serves. Its primary responsibilities are:
- To establish and maintain a secure, outbound connection to the ZTNA control plane.
- To await instructions from the control plane about incoming user connections.
- To proxy traffic from the ZTNA service to the internal application.
2. Core Principle: Outbound-Only Connectivity
The single most important security feature of the connector architecture is that it only ever makes outbound connections. This is a radical departure from traditional network security models.
In a classic VPN or perimeter-based model, you must open inbound ports on your corporate firewall to allow the VPN concentrator to accept connections. Each open port is a potential entry point for an attacker to scan and exploit.
The ZTNA connector model inverts this.
Microsoft Entra private network connectors - Security and networking
Let's start with a clear definition of this principle from Microsoft's documentation for their ZTNA connectors.
Please read the short 'Security and networking' section. Note the explicit statements that you do not have to open inbound ports and that connectors only send outbound requests. This is the key security advantage we are designing for.
How is this achieved?
Instead of listening for incoming connections, the connector proactively establishes a persistent, secure tunnel to a well-known endpoint in the ZTNA provider's cloud. This connection is initiated from inside the private network and traverses the firewall on standard outbound ports (typically TCP/443), which are almost always permitted.
Once this tunnel is established, it serves as a bidirectional communication channel. The control plane can send commands to the connector, and the connector can pass application traffic back to the user, all over this single, outbound-initiated connection. The firewall sees nothing but an outbound TLS session to a trusted cloud provider; the internal network remains completely invisible and inaccessible from the internet.
To see this in action, let's watch a segment that explains how Microsoft's ZTNA connectors function.
Deep Dive on Microsoft Entra Private Access
This video, 'Deep Dive on Microsoft Entra Private Access', provides a practical walkthrough of a connector-based ZTNA solution. It clearly illustrates the outbound connection model.
Please watch from 16:41 to 19:35. Focus on how the narrator describes the deployment of connectors inside the private network and explicitly states that 'these connectors are then establishing that connection... it's always out this way to the entra edge'. This demonstrates the outbound-only principle.
3. Secure Registration: Establishing a Cryptographic Identity
If the connector "phones home" to the control plane, how does the control plane know it can be trusted? Any piece of malware could try to impersonate a connector. This is where the secure registration process becomes critical. We need to provide the connector with a strong, verifiable, and non-reproducible cryptographic identity.
This process is a form of workload attestation. We must architect a flow that allows the connector, a software workload, to prove its identity to the control plane. The most robust way to do this is with Public Key Infrastructure (PKI), where the connector is issued a short-lived X.509 certificate that serves as its identity card.
The SPIFFE (Secure Production Identity Framework for Everyone) specification and its implementation, SPIRE (the SPIFFE Runtime Environment), provide the canonical, first-principles model for architecting this.
[PDF] Enabling Zero Trust Architecture (ZTA) with - OWASP Foundation
This presentation from the OWASP Foundation gives an excellent overview of using SPIFFE/SPIRE to establish workload identity. This is the theoretical foundation for our connector registration design.
Please read the following two sections: Start with 'Federated Identity – with SPIFFE and SPIRE' (slide 34) and continue to the end of 'SPIFFE & SPIRE' (slide 40). This will introduce the core concepts. Then, read 'Spire Server and Agent' (slide 42) and 'SPIRE Server Design Details' (slide 43). \nThink of the 'SPIRE Server' as our ZTNA Control Plane and the 'SPIRE Agent' as our ZTNA Connector. This reading details their exact responsibilities in the identity issuance process.
Drawing from the SPIFFE model and best practices, here is the architectural flow for secure connector registration:
-
Bootstrapping with a Join Token: An administrator, authenticated to the ZTNA management portal, generates a short-lived join token. This token is essentially a one-time password. The administrator includes this token in the connector's configuration file during installation.
-
Initial Attestation: The connector starts up and makes its first outbound connection to the control plane's registration endpoint. It authenticates this initial request using the join token.
-
Identity Issuance: The control plane validates the token. If valid, it performs several actions:
- It generates a new public/private key pair specifically for this connector.
- It creates an X.509 certificate (called a SPIFFE Verifiable Identity Document or SVID), embeds the public key, and assigns a unique identity in the certificate's URI SAN field (e.g.,
spiffe://my-ztna.com/connectors/connector-uuid-123). - It signs the certificate with its own private root CA key.
- It sends the certificate and the corresponding private key back to the connector over the secure channel.
- The join token is now invalidated and can never be used again.
-
Establishing the Secure Channel: The connector receives its new identity (certificate + private key) and stores it securely in memory or on disk. From this point forward, all communication with the control plane is authenticated using this certificate via mutual TLS (mTLS). The connector no longer needs the token.
This flow is confirmed by product documentation for real-world systems.
Microsoft Entra private network connectors - Connector authentication
Let's look at the Microsoft Entra documentation again to see how this certificate-based authentication is described in practice.
Read the 'Connector authentication' section. Notice the confirmation that client and server certificates are used, they are created during registration, and they are renewed automatically. This eliminates the need to store administrator credentials on the connector machine.
A crucial part of this design is the automatic, periodic rotation of these certificates. A well-architected system will have the control plane issue new certificates to the connector every few hours, ensuring that even if a certificate's private key were somehow compromised, its window of usefulness would be extremely limited.
4. Architectural Deep Dive
Let's assemble these principles into a more detailed architectural design.
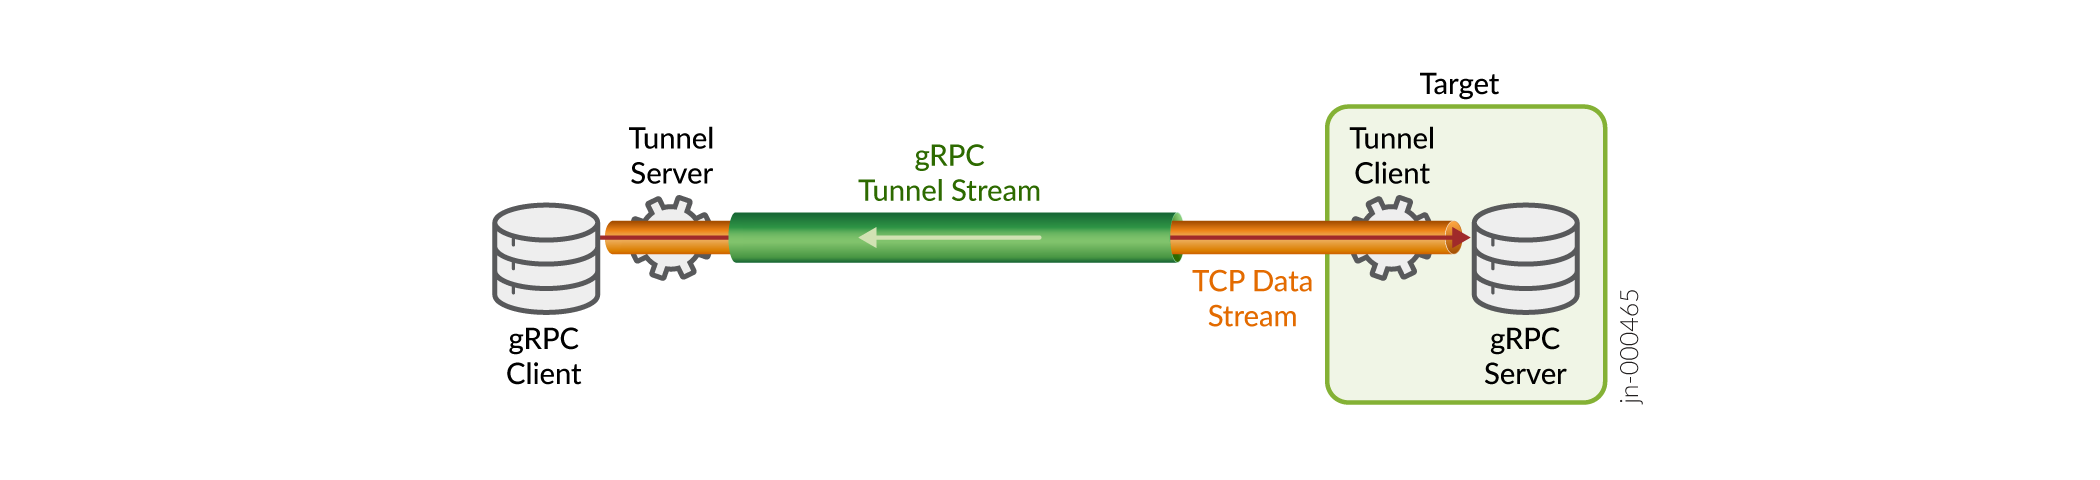
Communication Protocol: gRPC Tunneling
The outbound tunnel must be efficient, secure, and capable of handling multiple streams of communication. While a simple long-lived TLS connection would work, a more modern and powerful architecture uses gRPC (a high-performance RPC framework from Google) running over TLS.
This allows you to multiplex different types of traffic over a single TCP connection:
- A control channel for heartbeats and policy updates.
- Multiple data channels, one for each user-to-application TCP or UDP stream being proxied.
High Availability and Scalability
A single connector represents a single point of failure. To build a resilient system, we must run multiple connectors.
The architecture for this is connector groups.
- Multiple connector instances are deployed within the private network, ideally on different physical or virtual hosts.
- In the control plane, an administrator assigns these connectors to a logical group.
- This group is then associated with one or more applications.
When a user is granted access to an application, the control plane's load balancer selects a healthy, active connector from the assigned group to service the request. If one connector goes offline (due to a crash or maintenance), the control plane detects this (via missed heartbeats) and automatically routes new connections to the other connectors in the group, ensuring high availability.
Hardening the Connector's Environment
As a software engineer building this product, you must assume the connector itself could be a target. A defense-in-depth approach requires us to limit what a potentially compromised connector can do. The principle of least privilege applies not just to users, but to our own infrastructure components.
The ideal way to architect this is to place the connector in its own isolated network segment (e.g., a dedicated VLAN or subnet) and use an internal firewall to strictly control its outbound connectivity within the private network.
Secure Cloudflare Tunnels with vLANs and an Internal Firewall Before It's Too Late!
The following video, though focused on a home-lab setup with Cloudflare Tunnel (a commercial ZTNA connector), demonstrates this hardening principle perfectly. The architectural pattern is directly applicable to an enterprise-grade system.
Watch from 08:58 to 12:29. The creator places their Cloudflare Tunnel connector (running in Docker) onto a dedicated VLAN. Then, they configure an internal firewall rule that only allows that connector to talk to a specific internal IP address (the application server) on a specific port. This is an excellent demonstration of applying micro-segmentation to the ZTNA infrastructure itself.
This design ensures that even if an attacker were to exploit a vulnerability in the connector software itself, they would be trapped in a network sandbox, only able to communicate with the pre-approved applications, and unable to perform lateral movement across the internal network.
Conclusion
In this lesson, we have designed the ZTNA connector, the crucial component that securely connects private applications to the cloud-native ZTNA service. By focusing on first principles, we have built an architecture that is both secure and resilient.
Key Takeaways:
- Outbound-Only is Paramount: The connector's security model is built on initiating outbound connections to the control plane, eliminating the need for open inbound firewall ports and hiding the private network from the internet.
- Identity is Cryptographic: Connectors are not trusted by default. They must securely register with the control plane using a bootstrapping process (like a join token) to obtain a short-lived cryptographic identity (an X.509 certificate). All subsequent communication is secured with mTLS.
- Connectors are Grouped for Resilience: Deploying multiple connectors in a logical group provides high availability and scalability. The control plane manages load balancing and failover between them.
- The Connector Itself Must Be Secured: Applying the principle of least privilege, the connector should be deployed in an isolated network segment with strict firewall rules limiting its access to only the specific internal applications it is meant to serve.
Preview of the Next Lesson:
We have now designed the connector's control channel and its secure registration. But how does the actual user data flow from their device, through the ZTNA service, through the connector, and to the application? In our next lesson, we will design the reverse proxy and secure tunnel establishment for the ZTNA data plane, evaluating protocol trade-offs (e.g., TLS vs. WireGuard). We will architect the full data path that a user's traffic takes once the policy engine has approved their request.